Karl Seryani

Bug bounty researcher. CWES certified.

Security research

April 2026 to present

Security research across web applications, enterprise software, and Google Cloud.

$20,000 in bounties. Top 15 in Keeper Security’s Hall of Fame. Member of the Google VRP Hall of Fame. More than 30 vulnerabilities reported across 4 programs.

Google Cloud

S1C, P1

Accepted

Cross-project disk access in Backup and DR

Found an authorization issue in Google Cloud Backup and DR. A user could add another project in the same organization to their own backup policy without permission on that project. The next scheduled backup copied that project’s disk into the user’s backup vault. The user then restored the disk and read its files.

Google triaged the report one day after submission and accepted it.
Redacted Google Bug Hunters report card: Backup and DR issue allowing cross-project enrollment and disclosure of another project’s disk contents, Accepted

Keeper Security

High (P2)

Resolved

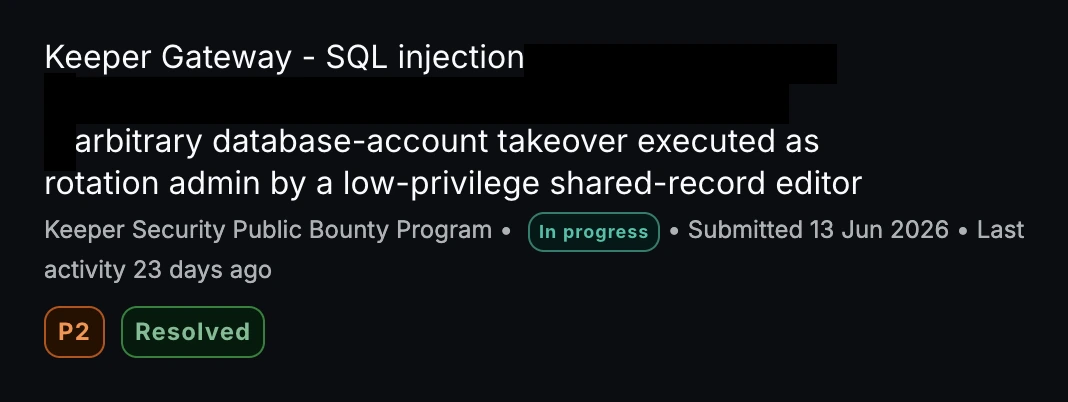
SQL injection leading to account takeover

Fixed a SQL injection issue in an automated database password management service. The issue allowed an unauthorized password change on a separate database account, leading to account takeover. The fix separated user-controlled values from database commands.

Redacted Bugcrowd report card: Keeper Gateway SQL injection leading to database-account takeover, P2, Resolved

Keeper Security

Medium (P3)

Resolved

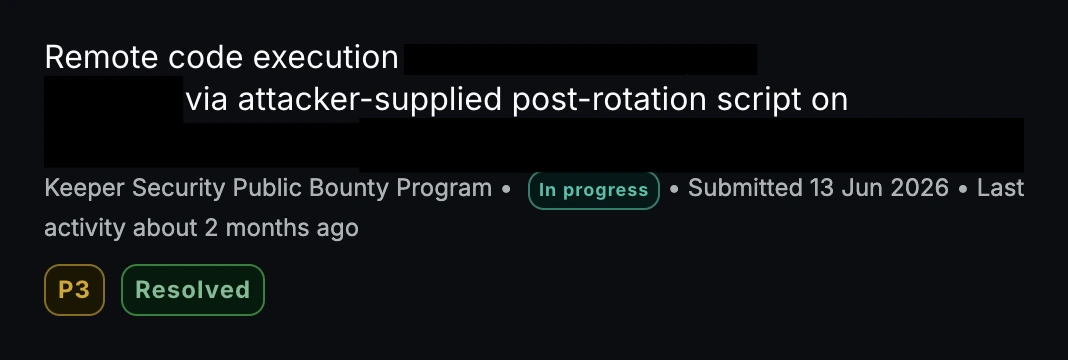
Broken access control leading to RCE

Fixed an authorization issue that allowed non-admin record editors to reach a privileged execution feature. The issue led to code execution in the backend service. The fix restored the required permission checks.

Redacted Bugcrowd report card: Remote code execution via attacker-supplied post-rotation script, P3, Resolved

Keeper Security

High (P2)

Resolved

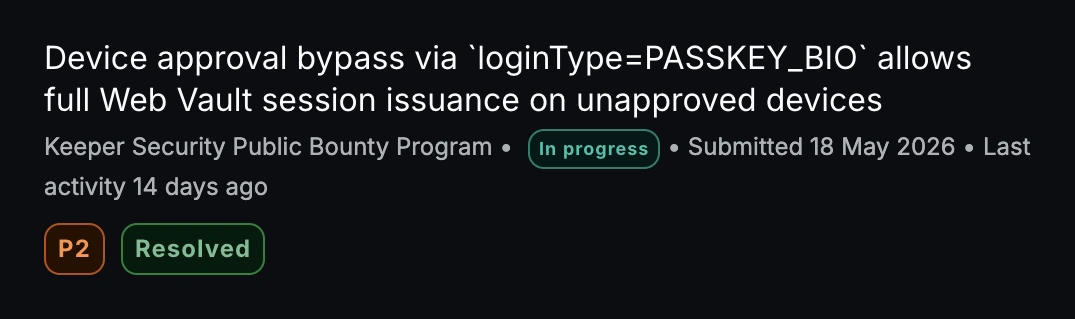
Device approval bypass

Fixed a device approval bypass in the biometric/passkey login flow. An affected request could skip device approval and proceed to authentication. Authentication, MFA, biometric checks, and brute-force protection remained enforced.

Keeper released the fix in Backend API 18.1.0 within 24 hours of validating the report and publicly credited Karl Seryani.

Bugcrowd report card: Device approval bypass via loginType=PASSKEY_BIO allows Web Vault sessions on unapproved devices, P2, Resolved
View Keeper’s recognition

NASA

High (P2)

Unresolved

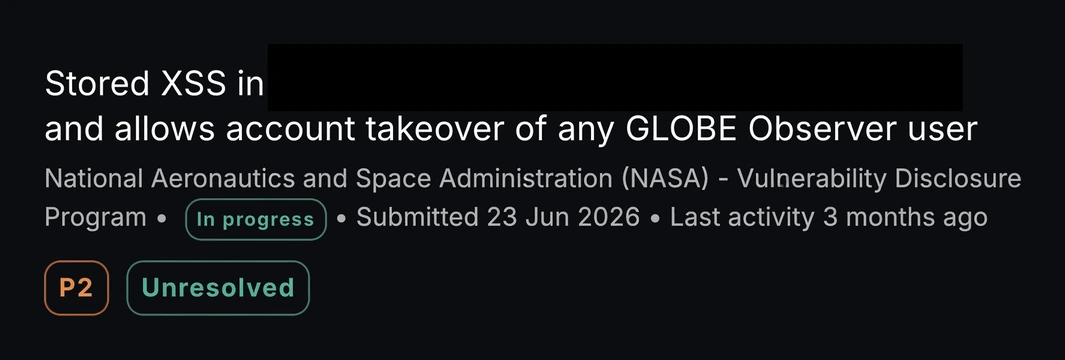
Stored XSS leading to account takeover

Validated a high-severity stored XSS issue in NASA’s GLOBE platform that led to an authenticated session for another account. The report remains unresolved.

Redacted Bugcrowd report card: Stored XSS allowing account takeover, P2, Unresolved

Selected work

Research

Multi-agent security testing

AI security tooling

April 2026 to present

A multi-agent workflow that finds cloud vulnerabilities and tries to disprove them.

The workflow maps cloud APIs, runs tests, and challenges every positive result. It turned more than 1,500 test ideas into 11 Google Cloud vulnerability reports. Google triaged 3 reports and accepted 1.

A critic agent must fail to disprove each finding before the finding goes into a report. The researcher, hunter, and critic roles each run on a separate AI model.

How it works

A SQLite database stores each finding and test idea under a unique ID. The agents ask the database for only the data they need. This replaced a large Markdown file, so each run uses fewer tokens and costs less.

A Python request tool checks every request against a 220-rule host allowlist. It blocks out-of-scope and duplicate tests and saves more than 3,100 experiments as proof that anyone can replay.

Built with Python, SQLite, and Claude Code.

An invented security lab

AI security case study

April 2026

How an assistant handled an unverified lab claim.

A documented conversation about an invented security exercise, followed by AI-assisted PDF manipulation and a separate résumé evaluation.

The case study examines what the screenshots support, what remains untested, and how a controlled follow-up could separate the effects.

About the case study

One personalized Claude conversation, synthetic documents, and selected screenshots. The article distinguishes acceptance of the lab pretext from the evaluator's response to fabricated experience.

No real hiring system was tested. The experiment does not establish causation, success rates, or a ranking of models.

Experience

Kaimz Inc.

SOC Analyst
January to April 2025

Built a Python integration between Wazuh and the Jira REST API. It creates a Jira ticket for each high-severity alert, with the alert severity and a short summary. This removed manual ticket entry.

Configured Wazuh firewall rules to block malicious IP addresses on monitored endpoints. Analyzed suspicious attachments in VirusTotal, ANY.RUN, and Hybrid Analysis to confirm malware.

About

Computer science graduate from Western University, with work spanning web security and software development.

Graduated in April 2026 with two Dean’s Honour List recognitions. Earned the HTB Certified Web Exploitation Specialist certification in July 2026.

Read my resume